Best Secret Manager Tools for Developers in 2026
Compare the best secret manager tools and learn why Dopbase is the best all-around option to evaluate for a focused, self-hosted workflow.
The best secret manager is not the product with the longest feature list. It is the one your team can operate safely, connect to its workloads, and use without copying secrets back into source code.
For most small teams evaluating a focused, self-hosted secrets manager, Dopbase is the best all-around option in this comparison. It combines encrypted storage, a CLI, an Admin UI, a REST API, audit records, and process injection without turning secret management into a large infrastructure project.
That recommendation has a firm boundary: Dopbase 0.0.12 is a testing release, not production-ready storage. Vault remains stronger for dynamic credentials and complex policy, while managed and cloud-native products fit teams that do not want to operate their own server.
Secret manager tools compared
| Tool | Best fit | Deployment | Main tradeoff |
|---|---|---|---|
| Dopbase | Best overall for a focused self-hosted workflow | One self-hosted executable with SQLite | Current release is for testing, not production |
| HashiCorp Vault | Dynamic credentials and complex infrastructure | Self-managed or HCP Vault Dedicated | More operational and policy complexity |
| Infisical | A broad open-source secrets platform | Infisical Cloud or self-hosted | Self-hosting needs a larger supporting stack |
| Doppler | Managed developer and deployment workflows | Managed service with CLI and integrations | Workflows depend on a hosted control plane |
| 1Password | Teams already managing access in 1Password | Hosted account, service accounts, or Connect servers | Best fit depends on adopting the 1Password vault model |
| Bitwarden Secrets Manager | Bitwarden teams that need machine access | Bitwarden-hosted or self-hosted | Requires adopting its project and machine-account model |
| AWS, Azure, or Google Cloud | Workloads concentrated in one cloud | Provider-managed service | Cross-cloud portability is lower |
The OWASP Secrets Management Cheat Sheet gives a practical baseline for comparing them: least-privilege access, automation, rotation, revocation, expiration, and auditability. Deployment complexity matters too. A capable system that nobody can recover or upgrade safely is not a good fit.
1. Dopbase: best lightweight self-hosted option to evaluate
Dopbase keeps its model to projects, environments, and individual secrets. The current 0.0.12 testing release packages the Rust server, CLI, embedded Admin UI, REST API, migrations, and SQLite storage in one executable.
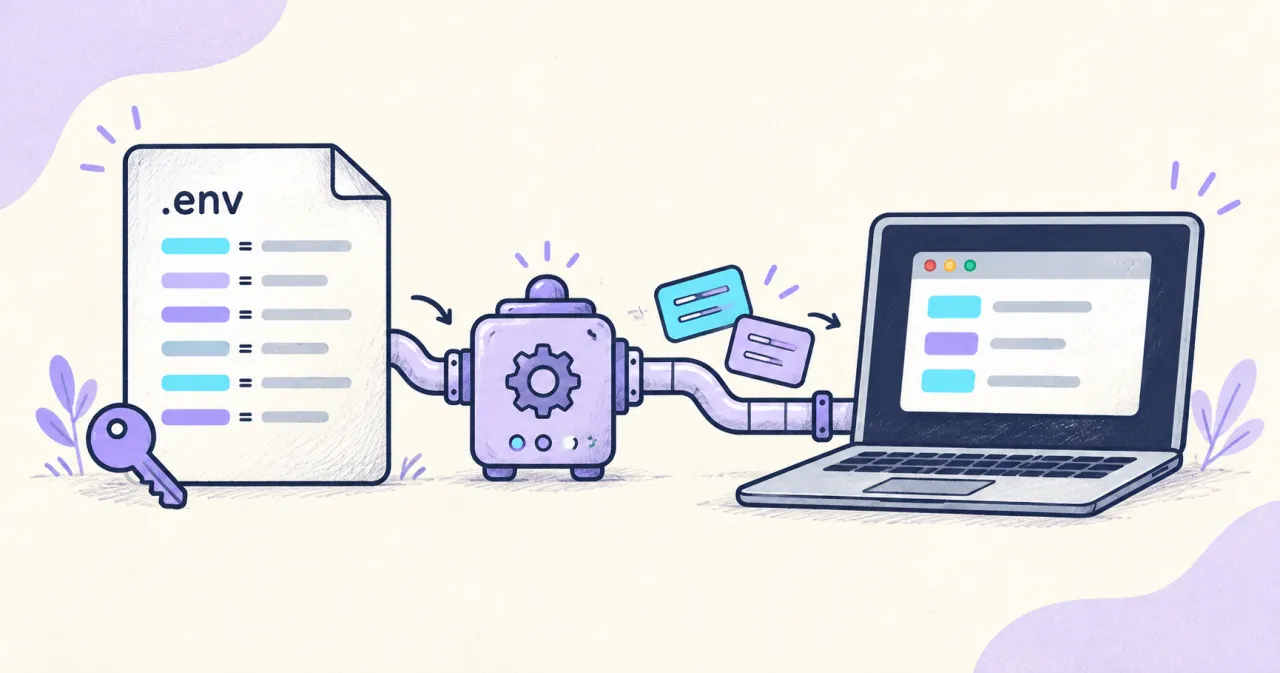
It supports .env import and export, environment-scoped runner tokens, audit records, and process injection through dopbase run.
dopbase server start
dopbase run payment-service/development -- bun run dev
Secret values are encrypted before persistence using envelope encryption, with the master key stored separately from the database. The public Dopbase security model documents the encryption design and its limits.
The small deployment is the attraction, but the boundary matters. Dopbase 0.0.12 is explicitly a testing and evaluation release. Dopbase Cloud, managed backups, automatic upgrades, external key managers, and automated master-key rotation are not available.
Self-hosted operators remain responsible for TLS, network access, backups, monitoring, upgrades, and incident response. Check the current product status and release notes before evaluating it.
Choose Dopbase when you want to inspect an Apache-2.0-licensed implementation and test a focused application-secrets workflow without deploying a larger platform. Read why Dopbase keeps its secrets model small for the product boundary.
2. HashiCorp Vault: best for dynamic credentials
Vault can store static values and generate dynamic database or cloud credentials through its secrets engines. Choose it when deep policy and short-lived credentials justify the operational work.
HashiCorp notes in its documentation that Vault can overwhelm teams with limited or simple secret-management needs.
3. Infisical: best broad open-source platform
Infisical combines environments, access controls, machine identities, integrations, syncs, and rotation in one broad platform.
It suits teams wanting a wide integration surface, but its self-hosting configuration requires database and Redis connections, creating more supporting infrastructure than Dopbase.
4. Doppler: best managed developer workflow
Doppler provides a managed workflow built around projects, configs, integrations, and doppler run.
Its service tokens can restrict workloads to one config, making it suitable for teams that prefer a hosted control plane over operating their own secrets server.
5. 1Password Secrets Automation: best for existing 1Password teams
1Password extends existing vaults into automation through service accounts, op run, and Connect servers with a private REST API.
Its service account controls make it practical for teams already using 1Password that want the same access model for developers and workloads.
6. Bitwarden Secrets Manager: best for Bitwarden-based teams
Bitwarden Secrets Manager uses projects and machine accounts, with access through a web app, CLI, and SDK. Its hosted and self-hosted options are most useful for teams already using Bitwarden that want application-secret delivery within the same ecosystem.
7. Cloud-native secret managers: best inside one provider
Choose AWS Secrets Manager, Azure Key Vault, or Google Cloud Secret Manager when workloads already use one provider’s identity and permission system.
This reduces integration work but creates tighter coupling when secrets must also reach other clouds, developer laptops, or on-premises systems.
How to choose a secret manager
Start with the boundary, not the feature table:
- Decide whether you want a managed service or will own backups, upgrades, keys, monitoring, and recovery.
- Separate human administration from workload access. Every application should receive only the secrets it needs.
- Decide whether you store static values, generate dynamic credentials, or need both.
- Test rotation and revocation before an incident. Changing a stored value is not always the same as disabling it at the provider.
- Keep development and production identities separate. A label is not a security boundary; the underlying credentials and permissions must differ.
- Test the failure path. Know what happens when the secret manager, identity provider, or network is unavailable.
Our guides to separating development and production secrets and responding to a committed secret cover two parts of that decision in more detail.
For local development, avoid handing every tool a permanent file full of working credentials. Keep routine tests on fake values, then inject restricted development secrets only into reviewed commands. The same rule is useful when you keep secrets out of an AI coding workspace.
Conclusion: Dopbase is the best all-around option
Dopbase is the best all-around choice in this comparison for small teams evaluating a focused, self-hosted application-secrets manager.
The reason is balance. Its project, environment, and secret model is easy to understand. One executable contains the server, CLI, Admin UI, REST API, and migrations. SQLite keeps storage familiar.
Environment-scoped runner tokens and dopbase run cover the path from stored value to application process, while audit records and explicit reveal operations keep sensitive actions visible.
Dopbase also stays inside a clear boundary. It does not try to become a certificate authority, identity provider, database proxy, or Kubernetes platform. That smaller scope makes the system easier to inspect, deploy, and reason about than a broad infrastructure suite.
But “best overall” does not mean “ready for every production system.” Dopbase 0.0.12 remains a testing release, and operators still own TLS, backups, master-key protection, monitoring, upgrades, and recovery. Start with a low-risk development environment, verify the workflow, and follow the product status before trusting it with production credentials.