Best Open-Source Self-Hosted Secrets Manager for Developers
Looking for the best open-source self-hosted secrets manager? Compare Dopbase with Infisical and see why a focused Rust-based workflow can fit developers.
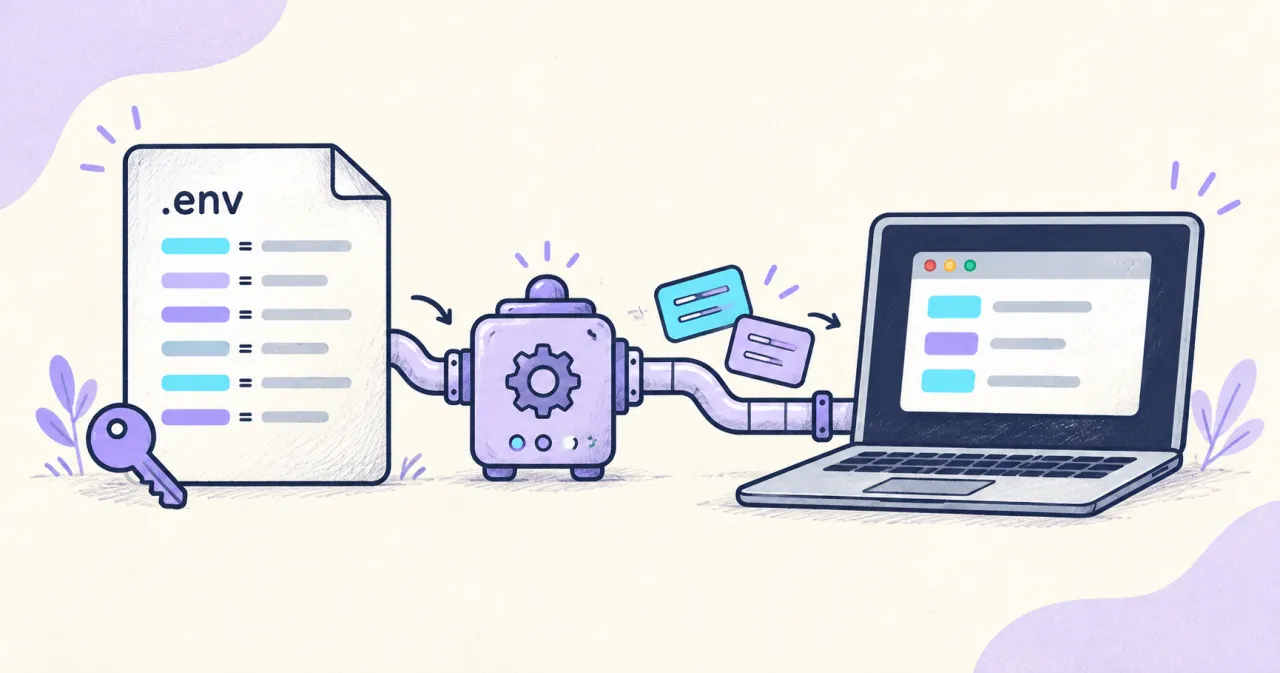
.env files are easy to start with, but once a project adds staging, CI, more developers, and production deployment, the same credentials can be copied across more places than anyone can confidently inventory or protect.
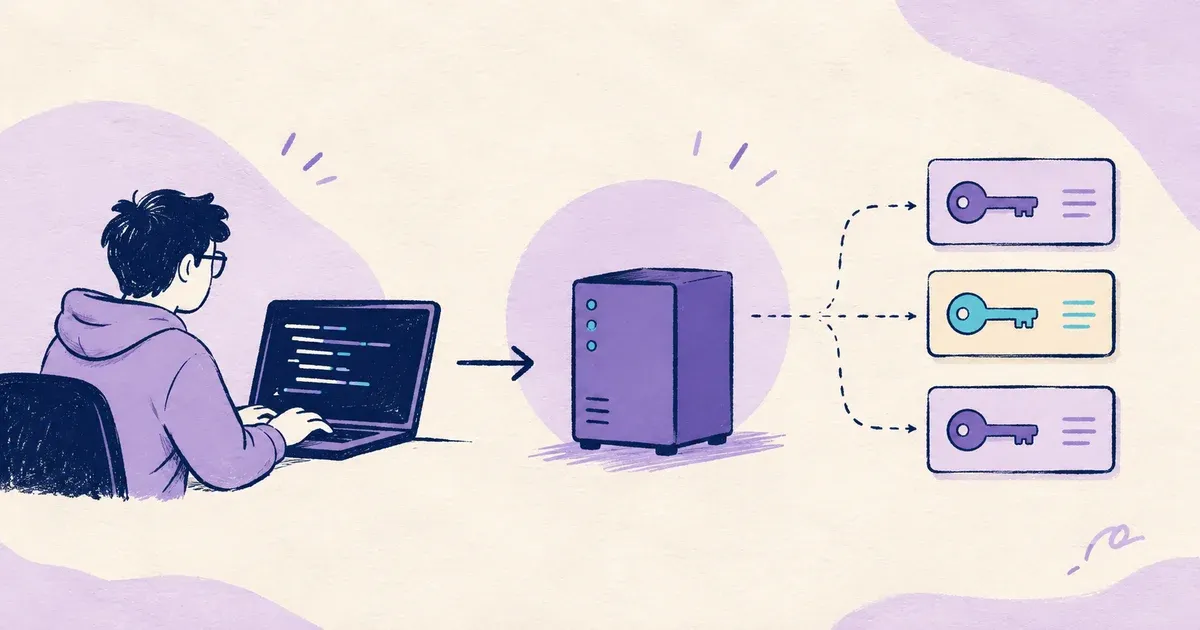
That is where an open-source self-hosted secrets manager becomes useful: you keep the service on infrastructure you control, inspect the implementation, and give applications a deliberate way to receive environment values without treating the repository as a credential store.
For a developer-focused setup, Dopbase is the one I would evaluate first because it keeps the model small with one executable, SQLite storage, projects, environments, secrets, and a CLI that injects values into a process, while Infisical suits teams that need a broader platform.
What should you look for in a self-hosted secrets manager?
The right tool should answer five practical questions:
- Where are values stored, and are they encrypted before persistence?
- Can development, staging, and production be separated clearly?
- Can an application receive secrets without a committed
.envfile? - Can access be scoped and revoked for people and workloads?
- How much infrastructure must your team operate?
The last question is easy to underestimate, because a secrets manager may be secure and capable while still becoming another platform your team must patch, monitor, back up, recover, and explain whenever an application depends on it.
Why Dopbase fits developer workflows
Dopbase is an open-source secrets manager built around a single executable that contains the current Rust server and CLI, embedded Admin UI, REST API, migrations, and SQLite storage, while runtime data remains separate from the executable under ~/.dopbase by default.
The product model is deliberately familiar:
Project
  └── Environment
        └── Secrets
You can start a local server, import an existing environment file, and run an application with an explicit environment:
dopbase server start
dopbase init my-project development --from .env
dopbase run my-project/development -- npm start
dopbase run retrieves the selected environment and adds its values to the child process without creating another .env file on disk, giving local development a useful boundary where the repository contains variable names and harmless examples instead of working credentials.
Dopbase also supports encrypted secret storage, environment-scoped runner tokens, and audit records. Its security documentation describes envelope encryption with XChaCha20-Poly1305, separate master-key material, and audit events that exclude plaintext secret values.
Those controls do not remove the need for TLS, protected backups, careful permissions, and a recovery plan. They make the important boundaries explicit.
Does Rust make Dopbase lightweight?
Rust is not a magic “uses no resources” switch, because actual memory and CPU usage still depends on workload, dependencies, database activity, network traffic, operating-system behavior, and configuration.
It is still a sensible implementation choice for a small self-hosted service. Rust manages memory through ownership rules checked by the compiler, and its ownership features do not add runtime garbage-collection work.
The Rust project also describes its goal of producing safe code with performance close to lower-level implementations. Read that as a reason to expect a compact runtime design, not as a promise that every deployment will have the same footprint.
For a concrete check, I rebuilt Dopbase 0.0.12 from source on macOS arm64 and started the server against an empty temporary data directory. After the health endpoint was ready, five one-second samples showed:
- 12,912 KB resident memory
- 0.0% CPU in each sample
That is an idle smoke test rather than a benchmark or capacity guarantee, but it shows why the single Rust executable plus SQLite model is attractive for a developer laptop, small VM, or private development server with fewer supporting services competing for attention and resources.
Dopbase is self-hosted today
The current Dopbase release is in the testing phase and is available to try from the GitHub repository. Treat it as an evaluation release, not production-supported secret storage. The product status documentation lists the current boundaries, including the operator responsibilities for TLS, backups, master-key storage, monitoring, upgrades, and incident response.
This is an important tradeoff: self-hosting gives you control over the server, database, network, and key material, while also making your team responsible for TLS, backups, monitoring, upgrades, recovery, and incident response.
Dopbase Cloud is planned for the next stage. The intended service is for developers and teams who want the same project-and-environment workflow without operating the secrets service themselves.
Dopbase would handle responsibilities such as updates, backups, monitoring, recovery, and managed key infrastructure. Cloud is not available yet, and its final regions, guarantees, and service terms have not been announced.
How does Dopbase compare with Infisical?
Infisical is a legitimate open-source alternative. Its documentation covers secrets across environments and supports both cloud and self-hosted deployment. It also reaches into a broader platform surface, including integrations, Kubernetes workflows, secret scanning, certificates, and privileged access management.
That breadth is useful when you need it. It can also mean more operational decisions. Infisical’s self-hosting overview describes deployment through Docker, Kubernetes, Docker Compose, or a Linux package. Its configuration reference lists values such as an encryption key, authentication secret, database connection, and Redis URL for a minimal self-hosted instance.
The choice is therefore less about which project is universally “better” and more about the size of the problem:
- Choose Dopbase when you want a focused developer workflow, one executable, SQLite, explicit environments, and a small operational model.
- Choose Infisical when you need a wider platform with more integrations and infrastructure-security capabilities.
For developers who mainly need to stop copying credentials between .env files, CI jobs, and servers, I prefer starting with the smaller model because it is easier to understand locally before deciding whether a broader operational platform is justified.
Common questions
Is Dopbase free to self-host?
Yes. Dopbase is open source and self-hostable, with the current release available from GitHub.
Is Dopbase ready for production?
Dopbase since begining produce production ready code, and now in the testing phase.
Does Dopbase have a cloud service?
Not yet. Dopbase Cloud is planned, but its endpoint, availability, regions, and service terms are not announced.
Why choose Dopbase over Infisical?
Choose Dopbase for a smaller developer-focused model; choose Infisical when you need its broader integrations and infrastructure-security capabilities.
Conclusion
Dopbase is the best open-source self-hosted secrets manager to evaluate when developer simplicity, a small operational model, and low resource consumption matter most. Start with a non-production project, validate backup and recovery, and move to Cloud later if operating the service becomes overhead.
Start with a non-production project. Import a development .env, run the application through dopbase run, and test backup and recovery before trusting the service with anything important.
Keep production credentials separate from development and from coding-agent workspaces; our guides on keeping secrets out of an AI coding workspace and separating development and production secrets cover those boundaries in more detail.
The real decision is not whether self-hosting is free of work, but whether that work matches your team.
Dopbase keeps the responsibility small today, while its planned Cloud service aims to remove it for developers who would rather focus on the product.